Europe Has One Breach Clock. The US Has Dozens — and the SEC May Make It Worse.
By Charles Redding, Founder, DLegendDigital — November 1, 2026
On October 2, 2026, another comment letter landed in the SEC's file on Regulation S-K. It was one of dozens that had arrived since the agency opened its cybersecurity disclosure rules for reconsideration back in January. Industry groups are asking the SEC to narrow, or scrap outright, the rule that gives public companies four business days to disclose a material breach. Nobody knows yet how it will land.
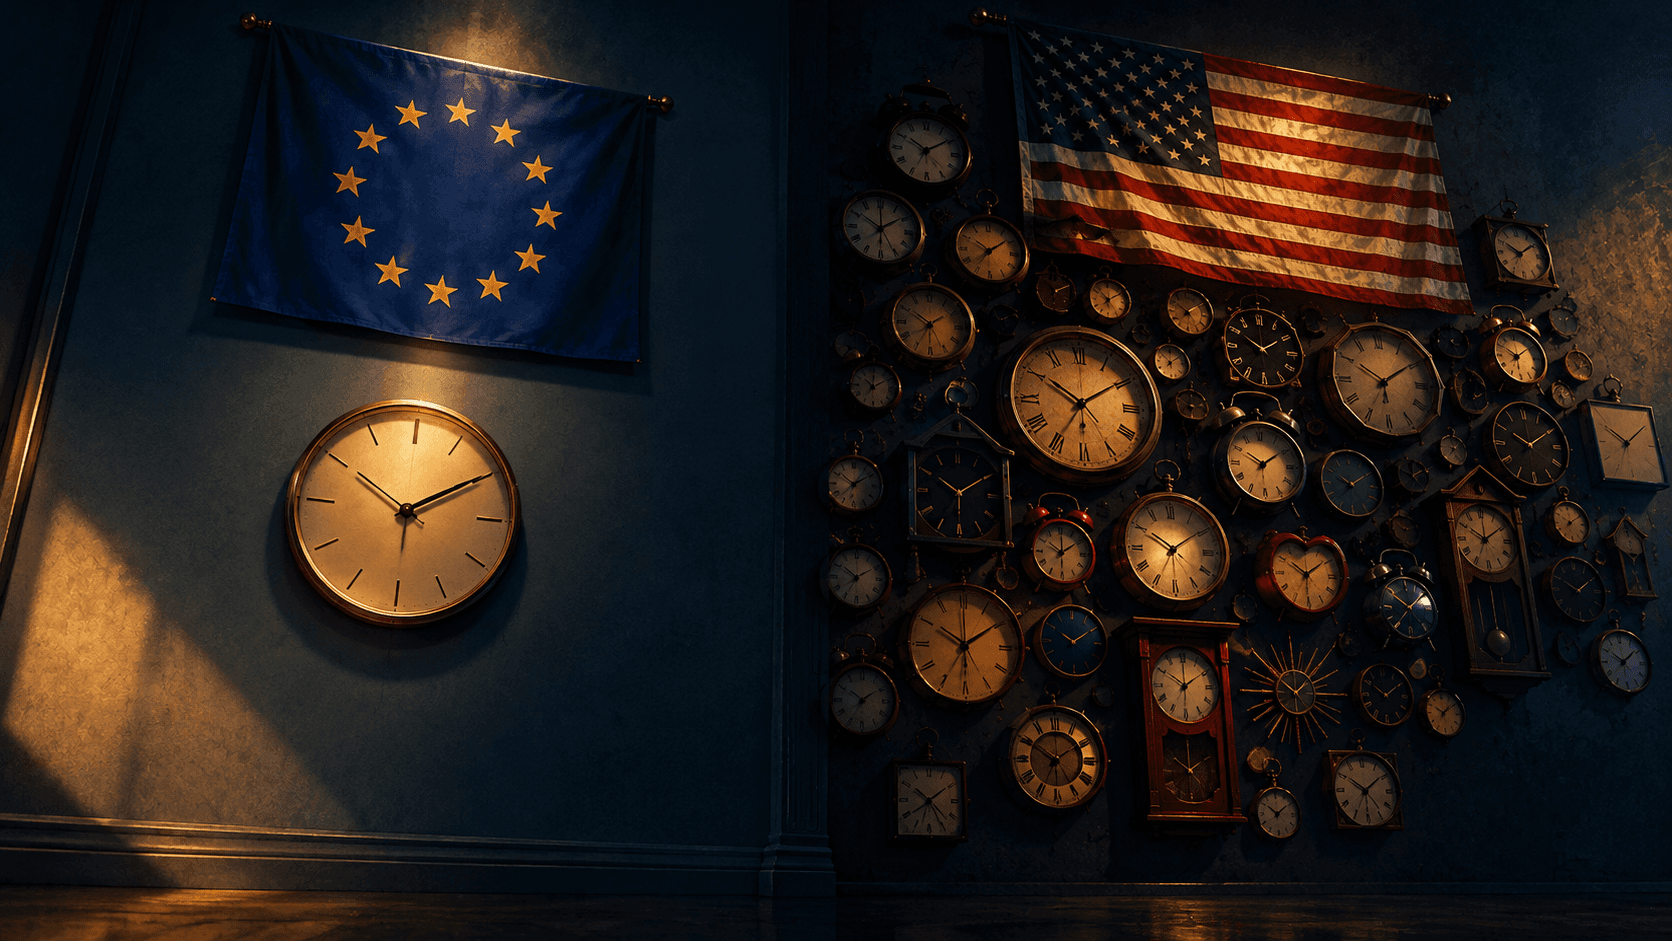
Six thousand miles away, nobody is writing that letter about Europe's rule. There's nothing to simplify. If you're covered by the General Data Protection Regulation (GDPR) and you have a breach involving personal data, you tell one regulator, within 72 hours, full stop. That's the whole rule. It has worked exactly the same way since 2018.
A US company handling the identical breach doesn't get that simplicity. It gets a stack: the SEC's rule, if it's public — a rule currently being argued over, not settled. A patchwork of fifty state notification laws that disagree on the deadline and on what starts the clock. Federal health-privacy rules if it touches medical records. State financial-services rules if it's a bank or an insurer. And soon, a brand-new federal rule for a long list of industries, still sitting on a desk in Washington waiting for a final signature.
Here's the part that should bother you more than any single deadline: even in the best case, where the SEC drops its rule entirely, you don't end up with one clock. You end up with one fewer clock out of a dozen. So what do you actually build when there isn't one deadline to meet — there are many, and they don't agree with each other?
What Actually Happens the Moment You Know#
Start with the rule everyone in a European compliance role already has memorized, because it's the only one they need. Under GDPR's Article 33, if your company controls personal data — meaning you decide why and how it's used, as opposed to a vendor that just processes it on your behalf — and that data is breached, you notify your country's data protection authority (think of this as your single designated regulator, the same way a bank has one primary examiner) within 72 hours of becoming aware of it. If you can't gather all the facts in time, you can file in stages. If the breach genuinely isn't risky to the people whose data it was — say, it was already encrypted and the keys weren't touched — you may not have to notify at all. That's the entire decision tree. One deadline, one recipient, one set of rules regardless of whether you're a five-person startup with a handful of EU customers or a bank with branches in nine member states.
Now cross the Atlantic. If your company is publicly traded, the SEC's rule since December 2023 has required you to disclose a cybersecurity incident on a public filing (Form 8-K, the SEC's standard "something material just happened" form) within four business days — but the clock doesn't start when the breach happens. It starts the moment your company determines the incident is "material," meaning significant enough that an investor would want to know. That determination is itself a judgment call your legal and security teams have to make under pressure, and it's one the SEC can — and has — second-guessed after the fact.
That four-day rule is also, right now, the subject of a genuine fight. In April 2026, five of the largest financial-industry trade groups — the American Bankers Association, the Bank Policy Institute, SIFMA, the Independent Community Bankers of America, and the Institute of International Bankers — filed a joint letter asking the SEC to scrap the rule entirely, or at minimum narrow it and add legal protection for companies that disclose in good faith. Their argument: a prescriptive, standalone cybersecurity disclosure rule can hand attackers a roadmap and puts a disproportionate burden on smaller public companies. As of this writing, the SEC hasn't ruled on any of it. The four-day clock you're planning around today is the one you'll be living with tomorrow — plan for the rule as written, not the rule you're hoping for.
Below the SEC sits the part most executives underestimate: there is no single federal law requiring companies to tell consumers their data was breached. Instead there are fifty-plus separate state laws. Twenty states set an actual number of days. California, Colorado, Florida, New York, and Washington all require notice within 30 days. Alabama, Arizona, Indiana, New Mexico, Ohio, Oregon, Rhode Island, Tennessee, Vermont, and Wisconsin give you 45. Connecticut, Delaware, Louisiana, South Dakota, and Texas allow 60. The rest don't give you a number at all — they use language like "without unreasonable delay," which sounds generous until you realize there's nothing concrete to plan a response around. Texas adds its own wrinkle: even though consumers get 60 days, the state Attorney General has to hear about it within 30 if 250 or more Texas residents are affected. One breach, two deadlines, inside a single state.
Layer in the sector rules and the picture gets stranger, not simpler. New York's financial regulator (the Department of Financial Services, or DFS) runs its own cybersecurity rule, known by its regulation number, Part 500. If you're a bank, insurer, mortgage servicer, or several other kinds of licensed financial business in New York, you have to tell the DFS within 72 hours of determining a qualifying event occurred — the same 72 hours as GDPR, but triggered by a narrower, more deliberate decision rather than simply "becoming aware." Meanwhile, if you're a healthcare organization covered by HIPAA (the federal law governing medical privacy), you get up to 60 days from discovery to notify affected patients, and — depending on how many people were affected — either immediate notice to the federal Department of Health and Human Services or a once-a-year batch report. Sixty days is twenty times longer than 72 hours, for the same underlying act: somebody's sensitive information got out. A healthcare company licensed in both New York and California could be running NYDFS's 72-hour clock, HIPAA's 60-day clock, and California's 30-day consumer clock, all from one breach, all starting from a different moment.
And there's one more clock arriving. On October 1, 2026, the Cybersecurity and Infrastructure Security Agency sent its long-awaited final rule under the Cyber Incident Reporting for Critical Infrastructure Act — CIRCIA, a federal law aimed at sixteen industries the government considers critical, from energy to healthcare to communications — to the White House for a required review before it can take effect. That's a procedural step, not a finish line: the rule isn't in force, there's no compliance date yet, and the text can still change. As proposed, it would require covered companies in those sixteen sectors to report a "substantial" incident within 72 hours, and a ransom payment within 24. It will not replace any of the clocks above. It stacks on top of them. A Congressional Research Service review previously counted forty-five separate cyber-incident reporting requirements scattered across the federal government alone — CIRCIA becomes the forty-sixth, not a replacement for the other forty-five.
It's worth sitting with how long CIRCIA has taken to get even this far. CISA first targeted a 2025 finalization, missed it, retargeted May 2026, missed that too, and only reached the White House review stage in October 2026 — three years after the underlying law passed. That's not incompetence; it's a signal of how hard it is to write one federal rule that doesn't collide with the forty-five that already exist. If the agency tasked with writing a single new rule needed three years and multiple missed deadlines just to harmonize with itself, it says something about how unlikely a broader harmonization across the state and sector layers is anytime soon.
The Simplification That Isn't#
Here's the trap in watching the SEC fight play out: it's easy to assume that if the SEC backs down, the problem mostly goes away. It doesn't. The SEC's rule is one clock among a dozen a company might be running on a single breach. Winning that fight removes one line item from a very long list. The state patchwork doesn't move. HIPAA doesn't move. New York's regulator doesn't move. CIRCIA, whatever shape it finally takes, is still coming.
Compare that to Europe, where the equivalent fight simply doesn't exist, because there's nothing to fight about. A company with EU customers that wants to lobby for a simpler breach-reporting regime would be lobbying for the regime it already has. The lobbying effort in Brussels goes toward other things — what counts as personal data, how fines get calculated — not toward merging six disagreeing deadlines into one, because there was only ever one.
The uncomfortable comparison for a US-based company with any EU exposure: you may already be building the GDPR playbook as the "easy" one, and the American playbook as the hard one — when the real difference isn't that Europe's rule is lenient. GDPR's 72 hours is actually tighter than most of what's on the US side. The difference is that Europe decided on one number and stopped. The US has never had that conversation at all; it has had fifty-plus separate ones, at the state level, plus several more at the sector and federal level, none of which were required to agree with each other.
How This Impacts Your Organization#
The underlying principle holds regardless of your size: you are going to need one internal process that can satisfy the fastest, strictest clock that applies to you, and feed everything slower off the same set of facts. What changes by size isn't the principle — it's which clocks actually apply, how much room you have to build the process, and where your real leverage sits.
Large Enterprises (1,000+ employees)
If you're running a company this size, you almost certainly have a dedicated legal or compliance function already tracking most of these obligations individually. The real risk isn't that you miss a deadline outright — it's fragmentation. Your SEC disclosure team, your state-notification team, your sector-regulator team (NYDFS, HIPAA, or both), and whoever eventually owns CIRCIA reporting are likely different people, on different timelines, potentially drafting different public-facing language about the same incident. A regulator or plaintiff's attorney comparing your SEC 8-K language against your state breach letter for consistency is now a real exposure, not a hypothetical one.
Your leverage is scale: you can afford to build, staff, and rehearse a single incident-response trigger that feeds every downstream obligation from one set of confirmed facts, with one named owner deciding when the fastest clock (usually a sector rule like NYDFS, or GDPR if you have EU exposure) starts running. The concrete move: name one person — not a committee — who owns the "clock started" determination company-wide, and have your general counsel map, in advance, which of your business lines trigger which of the clocks above, so the mapping exists before the day you need it.
Mid-Size Organizations (100–999 employees)
Companies in this range are the most exposed to the coordination problem without having the staff Large Enterprises can throw at it. You likely carry at least one sector obligation (NYDFS if you're a regulated financial business, HIPAA if you touch health data) plus a state consumer-notification clock, and you may not have a general counsel's office big enough to run them as cleanly separate workstreams. The specific overcorrection to avoid here is building five different breach-response playbooks — one per regulation — because that multiplies the coordination problem instead of solving it.
Build one playbook, not five. Identify the single fastest clock you're realistically exposed to (for most companies this size, it's either a 30-day state deadline or a 72-hour sector rule if you're regulated), build your internal response timeline to that number, and treat every other filing as a byproduct of the same timeline rather than a separate project. Two more moves that don't require a dedicated compliance hire: get your outside counsel to send you, once, a one-page list of exactly which state and sector deadlines actually apply to where your customers and data live — not a generic fifty-state summary — and put a single named decision-maker (even if it's you) on call for the "has this become reportable" determination, because the biggest timeline risk at this size is the decision sitting unmade for days while people figure out whose job it is.
Small & Growing Organizations (under 100 employees)
If you're running a small or early-stage company, the honest starting point is that you probably don't know which of these clocks apply to you — and that's a bigger risk than any single deadline. A small e-commerce or SaaS business sells to customers in states it may never have mapped, which means it's potentially exposed to several different state clocks without realizing it, and the "without unreasonable delay" states are deceptively the hardest to handle with no legal staff, because there's no number to point to.
Don't build a reporting program you don't need yet — you almost certainly aren't subject to the SEC's rule (you're not public) or CIRCIA (you're very likely under its small-business size threshold), and spending scarce time replicating enterprise-grade incident-response bureaucracy is wasted effort at this stage. What you should do: find out, once, which states your customers actually live in and write down the single shortest deadline among them (most companies this size find it's 30 days once California is in the mix), encrypt anything sensitive you store so a breach of encrypted data may not trigger notification at all in many states, and if you have any EU customers, treat the GDPR 72-hour rule as your real floor regardless of how small you are — GDPR doesn't have a small-business exemption the way most US rules do.
What to Do Monday Morning#
- Name one person who owns the "clock started" decision. Not a committee, not "legal will figure it out" — one named individual whose job, when something happens, is deciding which obligations are now live and when they started. Do this before you need it, not during.
- Write down which states your customers actually live in. Pull your customer or user list and map it against the 30/45/60-day state tiers above. Most companies have never done this exercise and are surprised by what they find.
- Ask your outside counsel for a one-page, company-specific deadline map — not a generic survey. You want the specific sector, state, and federal rules that apply to your actual business, not a fifty-state summary you'll never use as written.
- If you have any EU customers or EU-based data processing, confirm your GDPR 72-hour playbook actually exists and has been rehearsed. Don't assume it's simple because the rule is short — a 72-hour deadline with no rehearsed process is harder to hit than a 60-day deadline with one.
- Check your encryption coverage on anything that would trigger a notification obligation if breached. Many state laws exempt properly encrypted data from notification requirements entirely — this is one of the few moves on this list that can remove a deadline from the table rather than just helping you hit it.
- If you're a public company, read the current SEC comment file before assuming the four-day rule is changing. Plan around the rule as it exists today. A rescission that may or may not happen is not a compliance strategy.
- Put one person in your organization in charge of watching the CIRCIA rule's progress toward finalization, and rehearse against your fastest clock, not your slowest one. CIRCIA isn't in force yet, but when it is, you'll want to already know whether your industry is on the covered list — not find out the week of your first incident. And whenever you do run an incident-response drill, most organizations quietly default to practicing against the most forgiving deadline on their list, because it's the easiest one to hit cleanly. Rehearse against the 72-hour clock instead — GDPR or NYDFS, whichever applies to you — and the slower deadlines take care of themselves.
If You Want a Place to Start#
If this reads like a coordination problem more than a legal one, that's because it is — the hard part isn't knowing that GDPR says 72 hours, it's building one internal process that can feed every applicable clock from the same set of confirmed facts without contradicting itself across filings. A NIST Cybersecurity Framework readiness toolkit built around the RESPOND function — specifically incident management and incident communication — is a reasonable starting point for that internal process, because it's designed around exactly this kind of multi-stakeholder response coordination rather than any single regulation. For organizations that want a second set of eyes on which specific clocks actually apply to their business before building anything, a short advisory engagement scoped to that question alone is often more useful than a generic compliance audit. This post stands on its own either way — the actions above don't depend on either offering.
The Uncomfortable Truth#
So what do you build when there isn't one deadline — there are many, and they don't agree? You build one internal process, anchored to the fastest clock you're actually exposed to, and you let every slower obligation ride on the same confirmed facts instead of running its own separate fire drill. That's true whether you're navigating two clocks or a dozen.
Over the next six to twelve months, expect the SEC fight to resolve one way or the other — narrowed, rescinded, or left alone — and expect CIRCIA to finally clear its White House review and start its own compliance clock running for sixteen industries that don't have one today. Neither outcome will simplify the picture as much as it sounds like it should. The US patchwork isn't the product of one bad rule that can be fixed; it's the product of fifty states, several sectors, and now a new federal law, none of which were ever required to talk to each other.
I've watched enough of these rules land to say this plainly: the company that gets hurt isn't usually the one that missed a single deadline. It's the one that told two different regulators two different versions of the same story, because nobody owned the moment the clock started. Fix that one thing, and the rest of the patchwork becomes a scheduling problem instead of a crisis.
— Charles Redding
About the author
Charles Redding
Founder of DLegendDigital. 35+ years of enterprise technology leadership across audit, risk management, cybersecurity, and AI. Former CIO, VP of Technology, and Director at organizations ranging from high-growth startups to $4.3B global enterprises.